Security leadership for your business

Security needsan owner.It doesn’t haveto be you.

You run the business. We lead the security program.

A clearer path to a stronger security program.

Practical security leadership

You don’t need
another list of
problems.
You need a way
forward.

Security decisions, customer requirements and compliance reviews can put new demands on a team that already has plenty to do. Vectari helps you work through them with your existing IT team or providers. You can also ask for penetration testing, public information searches into people and businesses you may work with, vendor reviews or passive security scans.

Requirements into a plan

Readiness starts with
what is in place.

Bring your customer request, contract requirements or target framework, along with your systems, current controls and available evidence. Start by agreeing what applies and what needs work.

A scope your team can act on.

Whether you are preparing for SOC 2, ISO 27001, CMMC or a customer security review, first agree the requirements and scope. Then put the gaps, owners and dependencies into a plan your team can use.

Take the first step

Clarity starts here.

Check a domain, review a link or work through your security priorities. No account required.

A path that fits your business

Start where you are.

You don’t need to know the service name.
Start with what’s on your mind.

Your next step / 01

Get security off your plate.

For leaders balancing security decisions with everything else. Start with clear ownership, then build a program your team can sustain.

A named security lead. A practical roadmap. A regular rhythm for progress.

Explore vCISO

Start with something useful

Find your starting priorities

Free assessment · 10 questions · Immediate guidance
Your next step / 02

Turn the deadline into a plan.

For teams facing a customer review or compliance milestone. Clarify the requirements, organize your evidence, and focus on the gaps that matter.

Clear requirements. Organized evidence. Owners for the next steps.

Explore compliance readiness

Start with something useful

Know what to bring to the review

Readiness guide · Requirements, records and team commitments

Your next step / 03

Know who you’re working with.

For researching a prospective business partner or vendor, reviewing your own public footprint or requesting a passive security scan. Start with the decision you need to make.

Findings with sources. Questions to follow up. Support for a business decision.

Explore searches & vendor reviews

Start with something useful

Request a free exposure review

Public exposure only · Eligibility confirmed first; person and vendor research quoted separately

Your next step / 04

Put your controls to the test.

For teams that need evidence of what can be exploited. Define the systems and permissions, then turn testing findings into practical fixes.

An agreed scope. Contextual findings. A remediation discussion.

Explore penetration testing

Start with something useful

Prepare a testing scope

Bring authorized targets, access, the customer request and report deadline

From uncertainty to a plan

Know where you stand.
Know what comes next.

01 / Understand

Start with your business.

We listen to the pressures, deadlines, and decisions you face. Then agree what needs attention.

02 / Prioritize

Make the next steps clear.

Translate risk into a realistic plan, with owners and priorities your team can act on.

03 / Move forward

Build lasting confidence.

Review progress, validate improvements, and adapt your program as the business changes.

Published perspectives & community education

Explore the thinking
behind the work.

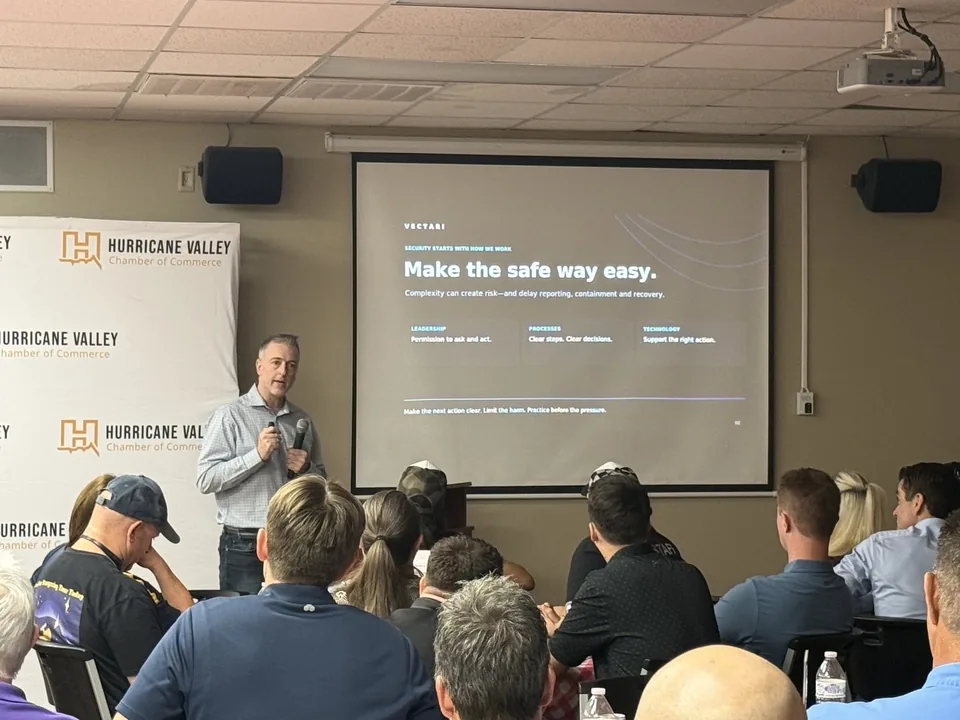
Jeremiah Udy presenting ‘Make the safe way easy’ at the Hurricane Valley Chamber of Commerce luncheon.
Photo: Hurricane Valley Chamber of Commerce

Speaking · September 17, 2026

Make the safe way easy.

Jeremiah Udy spoke at the chamber’s Cybersecurity Essentials luncheon in Hurricane, Utah. His presentation focused on clear steps, clear decisions and making security easier for the people doing the work.

See the chamber’s Facebook photo

September 17 event details

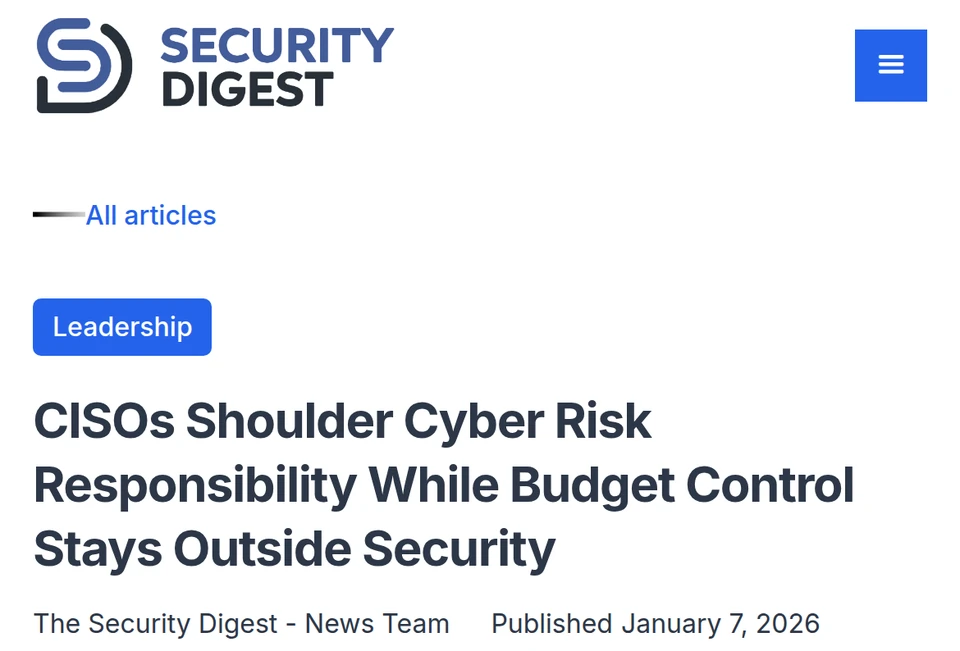
Screenshot of Jeremiah Udy’s interview in The Security Digest, with the article headline and publication date.
Screenshot: The Security Digest

Interview · January 7, 2026

Cyber risk, authority and accountability

In The Security Digest, Jeremiah discusses connecting risk ownership to decision-making authority and resources.

Read the published interview

A conversation, not a sales obstacle course

Let’s talk about what’s
on your plate.

Bring your questions. We’ll work out whether Vectari is the right fit.

Talk through your priorities

Prefer email? info@vectari.co